AI governance consulting that builds compliance into the system
Our AI governance consulting maps each AI system to the rules that apply, such as GDPR, HIPAA and the EU AI Act. We then build access control, audit logs, human review and model documentation into the software, so your compliance team can check how every answer was produced.
AI systems running in production
clients served since 2012
shipping software since 2012
on Clutch, from 33 verified reviews
countries with live clients
9001:2015 certified delivery process
Trusted by teams at
Clutch 4.8/5Verified client reviews
GoodFirmsReviewed software partner
ISO 9001:2015Certified delivery process
GDPR compliantData handled under EU rules
What AI governance consulting covers
Auditors ask to see controls working inside the system, so most of our governance work happens in the software itself.
- What is AI governance?
- AI governance is the set of rules, controls and records that decide how a business builds, uses and monitors its AI systems. It covers who can access which data, how outputs are reviewed by people, how decisions are logged and documented, and how each system is checked against laws such as GDPR, HIPAA and the EU AI Act.
Related: AI strategy decides which systems to build first. AI evaluation and observability measures whether they stay accurate.
EU AI Act compliance
The EU AI Act sorts AI systems into risk tiers, and the obligations grow with the tier. Your legal team decides how each system is classified. We build what that classification requires.
| Prohibited practices | High risk | Limited risk | Minimal risk | |
|---|---|---|---|---|
| Typical examples | Practices the Act bans outright, such as social scoring | AI used in areas such as hiring, credit decisions, medical devices or critical infrastructure | Chatbots and AI-generated content that people interact with | Spam filters, search ranking and most internal productivity tools |
| What the Act asks for | The system cannot be placed on the EU market | Risk management, data governance, technical documentation, logging, human oversight and accuracy checks | Transparency, so people know they are dealing with AI or AI-generated content | No specific obligations beyond existing law, with voluntary codes encouraged |
| What we build | We flag the risk during discovery and redesign the use case with you | Audit logs, review queues, model documentation and evaluation records designed into the build | Disclosure notices in the interface and labels on generated content | Standard access control and logging, ready if the use case later moves up a tier |
Healthcare and financial services carry their own rules on top of the Act. See how we handle them in healthcare software.
AI compliance services we deliver
AI compliance services that end in working controls inside the system, built by the same team that builds the AI.
AI system inventory
We build a register of every AI system you run or plan, with its purpose, data sources, users and owner.
Rules mapping
We map each system to GDPR, HIPAA, the EU AI Act and your sector rules, and your legal team makes the calls.
Gap review of existing AI
We audit a system already in use and list the controls it lacks against the rules that apply.
Access control
The AI reads only the records the signed-in user can open in the source system, with redaction of sensitive fields.
Audit logs
We record every prompt, response, model version, data source and reviewer decision and keep it for review.
Human review
Outputs that affect customers, patients or money go to review queues, and every approval and override is logged.
Model documentation
Each model gets documentation of its intended use, training and retrieval data, evaluation results, known limits and change history.
Evaluation records
Accuracy checks on test sets built from your own questions, kept as evidence for every release.
See AI evaluationResponsible AI consulting
We advise on bias checks, disclosure to users and escalation paths, and write them as rules your teams can follow.
Have an AI system your compliance team has questions about
Tell us what it does and which rules worry you. We will show you which controls it needs and roughly what adding them would cost.
How governance controls work inside the system
Four patterns give your compliance team evidence they can inspect, because the controls run in the software itself.
Permissions carried through
The user's identity travels with every request, and the AI only reads records that user can already open.
Redaction before the model
Personal and confidential fields are masked before any prompt leaves your environment, and restored only where policy allows.
Human review on decisions
Outputs that affect a customer, patient or payment wait in a queue until a named person approves or changes them.
Traceable answers
Each answer is stored with the model version, prompt, sources and reviewer, so an auditor can replay how it was produced.
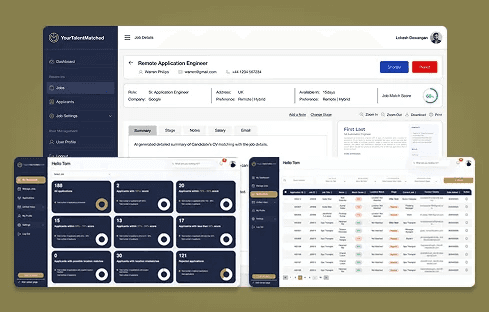
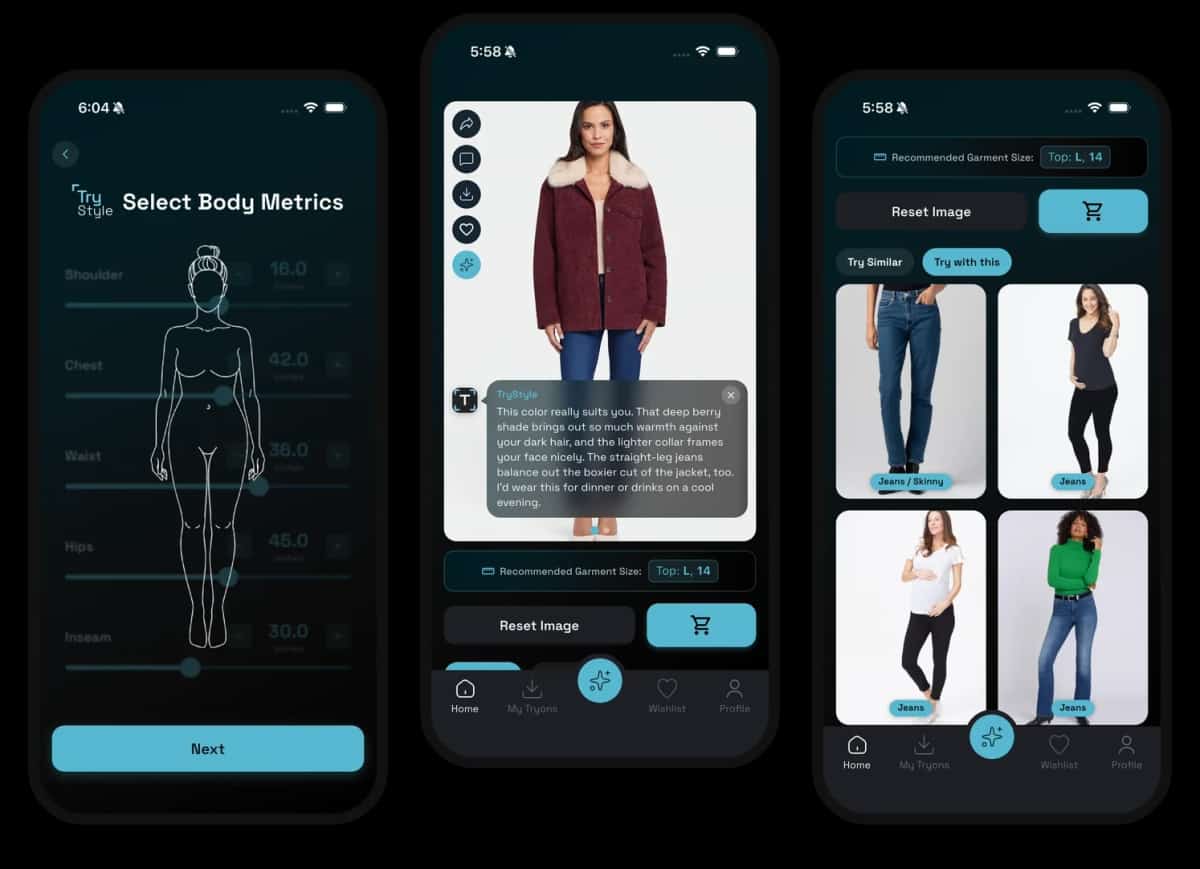
Talent Matched: AI candidate scoring inside a recruitment SaaS
Talent Matched keeps candidate data on a private LLM. Its AI agent can only get to recruiter data through MCP servers, and every customer's data lives in a separate schema. Each agent step and model call is traced. A recruiter still makes the final decision.
Ranking and shortlisting time, per the client
How an AI governance engagement runs
The governance discovery sprint takes 1 to 2 weeks. Controls for a new system are built into the production build, on the schedule the discovery plan sets.
One team, 14 years of shipping
projects shipped since 2012
AI systems running in production
clients across 45+ countries
years building software, since 2012
How we work with your legal and compliance teams
Your legal team interprets the law, and we build their decisions into the system as controls and tests.
Legal decides, we build
Your counsel makes the classification and policy calls. We give them the system facts they need to decide.
Controls priced in discovery
SOC 2, HIPAA and GDPR controls are written into the scope during discovery, so nothing is added late.
Your IP, under NDA
The code, documentation and audit records are yours from the first commit, and NDAs are standard.
One accountable team
The engineers who set up your controls also answer your auditor's questions.
What we put in place for AI regulatory compliance
Each control is built as part of the software and tested like any other feature.
AI governance for regulated industries
Sectors where an AI output can affect a patient, a customer's money or a legal position need the strongest controls.
Healthcare
- HIPAA-aware redaction
- Clinician review of AI drafts
Financial services
- Audit trails on credit and fraud models
- Human review of customer decisions
HR and recruitment
- Recruiter sign-off on AI scores
- Records of how candidates were ranked
Legal and compliance
- Confidential document handling
- Policy answers with sources
AI governance consulting cost
Most governance work starts with a free discovery sprint.
Governance discovery sprint
1 to 2 weeks and free, ending in a written proposal with a fixed quote. System inventory, rules mapping, gap review and a costed plan for the controls.
Best for teams that need to know what their AI systems require.
Controls built into a new system
Governance designed into a production AI build. Quoted and scheduled from the discovery plan.
Best for a new AI system headed for a regulated workflow.
Dedicated AI engineers
Senior AI engineers who add and maintain controls inside your repositories, from $2,499 a month per engineer.
Best for adding controls to several systems your team already runs.
Rated 4.8/5 by the clients we build for
Verified reviews from Clutch and GoodFirms, and clients on camera.
33 verified reviews on Clutch
 Clutch review★★★★★
“What sets ScalaCode apart is their technical AI expertise and an understanding of a client's organizational ethos.”
 GoodFirms review★★★★★
“They built a high-performance, AI-powered platform that transformed video engagement for learning.”
Clutch review★★★★★“What stood out to us as most impressive and unique about ScalaCode was their ability to humanize complex AI.”
Clutch review★★★★★“They managed to balance technical skill with an understanding of the marketing world.”
Clutch review★★★★★“Their team often proposed innovative features we hadn't considered.”
Clutch review★★★★★“They didn't just build an algorithm; they built a tool that respects the nuances of Indigenous reconciliation.”
Clutch review★★★★★“What I found impressive about ScalaCode was their ability to listen to the soul of an educational mission.”
AI governance consulting FAQs
We will answer anything not covered here on the call.
Does the EU AI Act apply to our AI systems?
It can apply to companies outside the EU when their AI systems are offered or used in the EU. Which obligations follow depends on the risk tier of each system, and your legal team decides the classification. We give them the facts they need, such as what the system decides, which data it uses and who sees the output. Sector rules for regulated buyers are covered under healthcare AI, fintech AI and legal AI.
What does an AI governance framework include?
An AI governance framework includes an inventory of AI systems, the rules each one must meet, and the controls that enforce them. In the software that means access control, audit logs, human review, model documentation and evaluation records. It also names an owner for each system and a review schedule.
Can you make an existing AI system compliant?
We can add the missing controls to a system another team built, after a technical audit. The audit lists gaps against the rules your legal team says apply, and we price each fix. Whether the system then meets the law is a judgment for your legal team and auditors.
How do you document AI decisions for auditors?
Every answer or decision is logged with the prompt, the model version, the sources it used and any reviewer who approved or changed it. Each model also has documentation covering intended use, data, evaluation results, known limits and change history. Auditors can trace a single output back to how it was produced.
How much does AI governance consulting cost?
AI governance consulting starts with a free 1 to 2 week discovery sprint. Building the controls is quoted from the sprint's plan. Dedicated senior engineers who maintain controls inside your systems start at $2,499 a month.
Do you work with our legal and compliance teams?
Yes, from the first week. Your legal and compliance teams decide which rules apply and how systems are classified, and we turn those decisions into technical requirements and tests. They review the documentation and audit records before launch.
Which regulations do you design AI controls for?
We design controls for GDPR, HIPAA and the EU AI Act, plus sector rules your compliance team names. SOC 2, HIPAA and GDPR controls are written into the scope during discovery. ScalaCode holds ISO 9001:2015 certification for its delivery process. Public bodies have extra rules of their own, covered under government and public sector.
Can our AI run without sending data outside our environment?
It can. Open-weight models such as Llama or Mistral can run in your own cloud or data centre, and sensitive fields can be redacted before any hosted model sees them. We choose the setup with your security team during discovery.
One team, matched to your working hours
We schedule 4 to 6 hours of daily overlap with US time and a full working day with the UK and Europe, so reviews, demos and fixes happen during your working hours.
What sets ScalaCode apart is their technical AI expertise and an understanding of a client's organizational ethos.
AI your compliance team can sign off on
- 30 minutes with the ScalaCode team
- Which rules your AI systems need to meet
- Which controls to build first and roughly what they cost
“Their approach, dedication and project execution played a critical role in TipStars' success.”
James Ellis, Founder, TipStars