Your React App Builds Successfully. That Doesn’t Mean It’s Secure
The News: React disclosed a critical remote code execution vulnerability affecting React Server Components on October 14, 2026. Patched releases include React
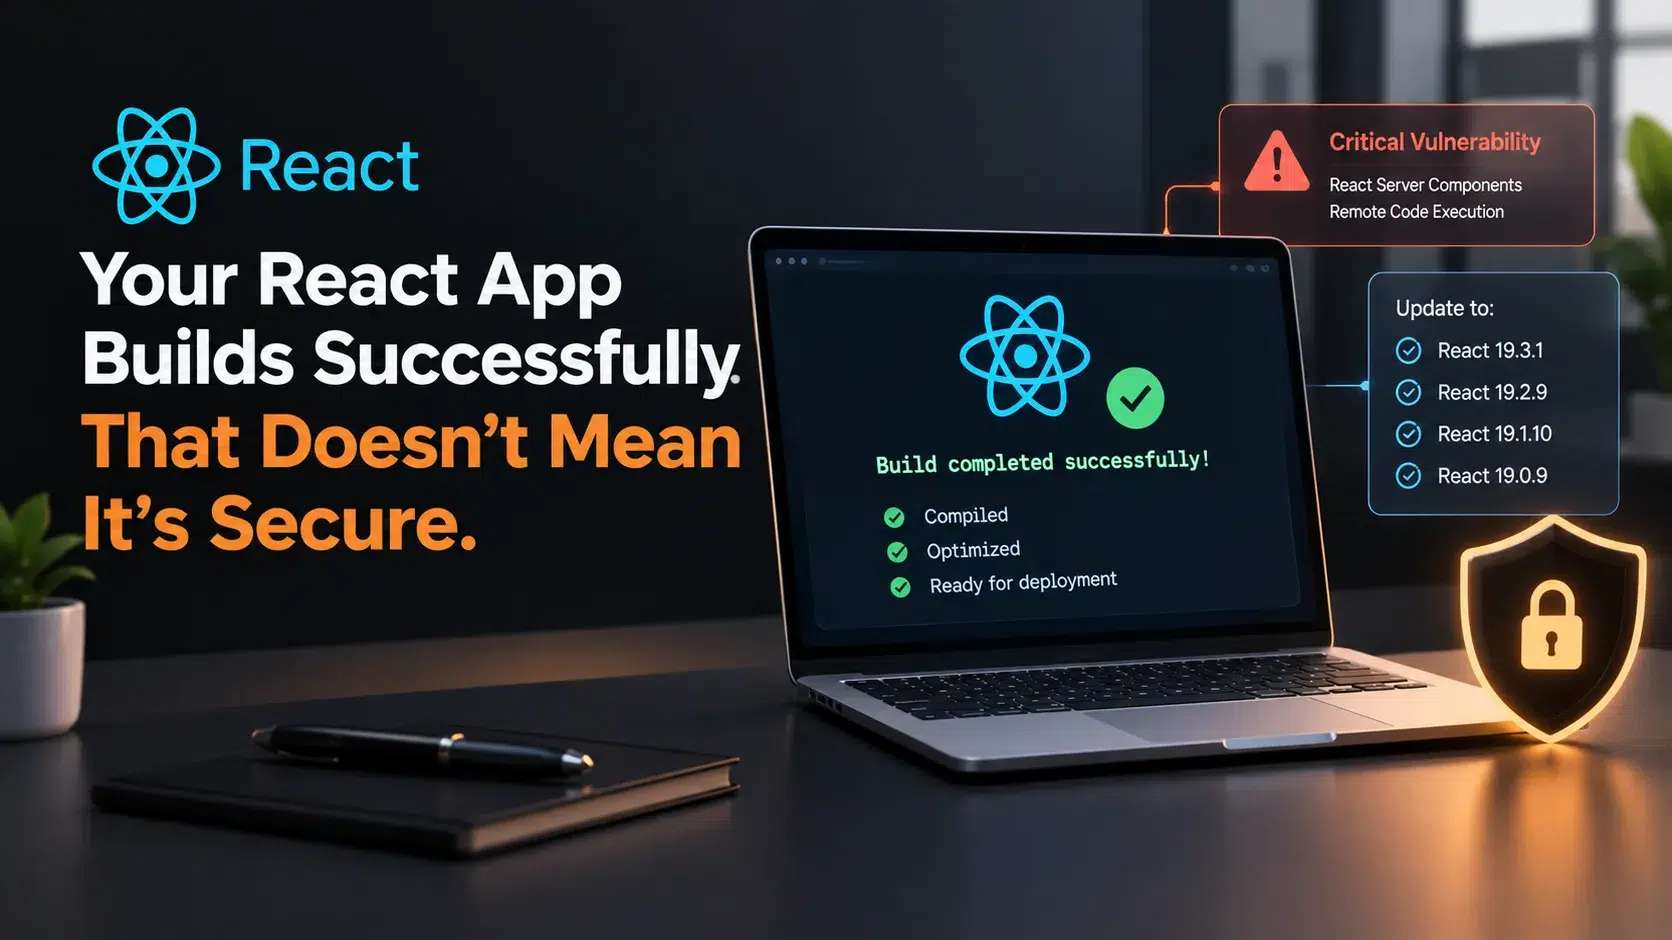
The News: React disclosed a critical remote code execution vulnerability affecting React Server Components on October 14, 2026. Patched releases include React 19.3.1, 19.2.9, 19.1.10, and 19.0.9. Next.js also published security updates for affected applications.
The Uncomfortable Truth About Modern Web Development
A successful build is not a security check.
On October 14, the React team disclosed a critical vulnerability in React Server Components that could allow remote code execution under specific conditions. The affected packages include react-server-dom-webpack, react-server-dom-parcel, and react-server-dom-turbopack.
The issue is serious. An attacker could craft requests that exploit the vulnerability without authentication when the affected conditions are present. The React advisory assigns it a CVSS score of 9.5 out of 10.
Here is the point: Shipping working software and shipping secure software are two different engineering responsibilities.
What This Means Outside React
Modern applications are built on dependency chains. React sits alongside frameworks, bundlers, plugins, APIs, and server-side infrastructure. A vulnerability in one layer can create exposure across the application.
This is particularly relevant for teams using React Server Components and frameworks such as Next.js. The Next.js team published patched releases, including versions 15.5.28 and 16.4.1, addressing critical upstream and framework-level issues.
The mistake is treating security updates as routine maintenance that can wait for the next sprint. They cannot all wait. A production application may handle customer records, business transactions, internal workflows, or sensitive operational data. When a critical vulnerability affects its stack, teams need to establish exposure, identify affected versions, patch appropriately, and verify the deployed result.
How Engineering Teams Should Respond
Three actions matter more than another round of feature development:
- Audit Dependencies: Identify React Server Components packages, framework versions, and affected production deployments.
- Patch and Verify: Follow the official advisories, upgrade to supported fixed versions, run regressions tests, and confirm the deployed environment actually uses the patched dependencies.
- Fix the Process: Maintain a software bill of materials where appropriate, automate dependency alerts, assign ownership for security updates, and define an expedited patching process for critical vulnerabilities.
One Important Distinction: The React advisory states that applications whose React code does not use a server are not affected by this particular vulnerability. Teams should assess their actual architecture instead of assuming every React application is exposed or assuming none are.
Quick Recap
In this post, the best engineering teams don’t wait for a security incident to review their codebase. They build security checks, dependency audits, and regression testing into the development lifecycle.
If your React application needs a security or quality review, explore ScalaCode’s Software Testing and QA Services to strengthen your testing process before the next release.
Smita
Customer Delight, ScalaCode
Smita heads the Customer Delight unit at ScalaCode and looks after client relationships while projects are under way. She studied computer science and has worked in technology and customer service for more than ten years. Her articles draw on that mix of technical and client-facing work.
Talk through your project with ScalaCode
- 30 minutes with the ScalaCode team
- What is realistic, what it costs and how long it takes
- You decide afterwards whether to build with us